Group Purchasing
Group Purchasing

Course Features

GIAC Security Essentials (GSEC)

Learn About Certification

46 CPE

Apply your credits to renew your certifications.

Essential Skill Level

Course material is for individuals with an understanding of IT or cyber security concepts.

23 Hands-On Lab(s)

Apply what you learn with hands-on exercises and labs.

MIL401N prepares Network Analysts through role-aligned, workflow-driven training mapped to DCWF/8140 requirements, covering packet analysis, DNS, NDR/NSM, and network defense.

MIL401N: Security Essentials for Network Analysts is a role-aligned training course for military and defense Network Analysts, aligned to DCWF and DoD 8140 workforce requirements, covering packet analysis, DNS, NDR/NSM, wireless, and network defense from architecture through active threat hunting.

A Purpose-Built Course for Network Analysts

MIL401N is purpose-built around the operational workflows, responsibilities, and readiness requirements of Network Analysts operating in military and defense environments, with training mapped to DCWF and DoD 8140 workforce requirements.

MIL401N is built around the discipline that sits closest to the wire: understanding how traffic moves, why it moves that way, and what it looks like when something is wrong. Students build deep capability in protocol and packet analysis, tcpdump filter writing, DNS architecture, and network detection and response (NDR) data sources, then extend that foundation into defense-in-depth, vulnerability management, cryptography, and the Windows, Linux, and cloud environments that traffic ultimately touches.

The course reflects how network defense operations have evolved. Students work directly with NDR and NSM data sources, hunt for adversary activity inside DNS traffic, and use tools including Snort3, Zeek, and Security Onion to detect intrusions, including the presence of adversary emulation frameworks such as Cobalt Strike. Scripting and automation skills carry throughout, so students leave able to move faster across Windows, Linux, macOS, and Microsoft cloud environments rather than relying on manual analysis alone.

The course is designed to support scalable workforce development across military and government organizations by aligning training directly to defined role requirements and operational outcomes. The emphasis is not simply on knowledge acquisition, but on preparing learners to operate effectively as the network-facing analyst inside a modern SOC or cyber defense team.

Hands-on labs reinforce this throughout. Rather than isolated technical exercises, the labs follow realistic operational scenarios requiring students to capture and interpret traffic, investigate DNS and NDR data, and apply defensive techniques across network, endpoint, and cloud environments. The result is a workflow-driven learning experience focused on building practical Network Analyst capability, not just course completion.

What You’ll Learn

  • Capture, filter, and analyze network traffic using tcpdump and Wireshark
  • Write custom tcpdump filters to isolate traffic of interest
  • Map DNS architecture and hunt for malicious DNS activity
  • Identify NDR and NSM data sources for network threat detection
  • Detect intrusions and adversary tooling using Snort3 and Zeek
  • Secure wireless networks and evaluate cloud and AI supply chain risk
  • Apply defensive controls across Windows, Linux, macOS, and cloud

Business Takeaways

  • Build scalable Network Analyst capability aligned to DCWF and 8140
  • Standardize network traffic analysis and DNS threat hunting practices
  • Reduce time-to-productivity for junior and transitioning analysts
  • Cut manual workload through built-in scripting and automation training
  • Strengthen readiness against network intrusions and adversary tooling
  • Deliver DCWF/8140-aligned training without building curriculum in-house
  • Develop analyst capability using realistic, hands-on network scenarios

Author Statement

“Modern military operations depend on interconnected systems, communications networks, cloud services, mobile platforms, and digital infrastructure more than ever before. These capabilities provide tremendous operational advantages, but they also expand the attack surface available to adversaries. As military organizations become increasingly dependent on technology, cybersecurity becomes inseparable from mission readiness.

At first glance, a growing number of cyber incidents might be attributed to the increasing complexity and connectivity of modern systems. Yet technology alone does not explain the challenge. Adversaries continue to succeed because they understand how to exploit weaknesses in people, processes, and technology. The battlefield may be evolving, but the importance of strong security fundamentals remains unchanged.

The reality is that today's military professionals must be prepared to operate in environments where networks are contested, communications may be disrupted, and cyber attacks can directly affect mission success. In these conditions, cybersecurity is not simply an IT problem; it is a readiness issue. The ability to understand, identify, and respond to cyber threats has become an essential component of mission readiness.

MIL401N is built around a simple principle: offense informs defense. By understanding how adversaries operate and how attacks affect systems, students gain practical, immediately applicable knowledge that strengthens resilience, improves decision-making, and enhances mission effectiveness.

Just as importantly, the course is continually updated to reflect the evolving threat landscape and lessons learned from the real-world. Cybersecurity does not stand still, and neither should training. The goal is not simply to understand today's threats, but to build the enduring fundamentals necessary to adapt to tomorrow's.”

— Bryan Simon, GSE, Course Author

Meet Your Authors

Course Syllabus

Overview

Every organization operates under the same reality: not every attack will be prevented, so detection depends on understanding how the network communicates. This section establishes defensible network architecture, then builds fluency in protocols and packet analysis, including writing custom tcpdump filters to isolate traffic of interest rather than relying on default captures. DNS architecture receives dedicated attention because DNS remains one of the most consistently abused protocols in modern intrusions, and understanding it is foundational to the DNS threat hunting introduced later in the course. NDR data sources and the practical issues analysts face in NDR/NSM programs round out the network-focused portion of this section, before extending into virtualization and cloud essentials, including software supply chain security, and closing with wireless network security, one of the most pervasive and least understood parts of most organizations' infrastructure.

Topic Details

  • An Introduction to MIL401N
  • Defensible Network Architecture
  • Protocols and Packet Analysis
  • Writing tcpdump Filters
  • DNS Architecture
  • Network Detection and Response (NDR) Data Sources
  • Practical NDR/NSM Issues
  • Virtualization and Cloud Essentials
  • Software Supply Chain Security
  • Securing Wireless Networks

Labs

  • Tcpdump
  • Writing tcpdump Filters
  • Security Onion Service-Side Analysis
  • Wireshark
  • AWS VPC Flow Logs

Overview

The section opens with information assurance: the foundational commitment to protecting the confidentiality, integrity, and availability of organizational systems. These properties are what adversaries specifically target, and understanding how large-scale threats attack each one makes the rest of this section actionable rather than theoretical. Identity and access management follows directly, since IAM is increasingly the security perimeter for cloud-based systems. Passwords remain the dominant authentication factor despite years of effort to move beyond them, and credential theft remains one of the most common entry points for attackers, so this module covers modern authentication methods, password security, and the role of IAM in a cloud-first environment. From there, the section turns to the frameworks that structure defensive decision-making: the CIS Controls, the NIST Cybersecurity Framework, and the MITRE ATT&CK knowledge base. Network defensibility then returns to focus through data loss prevention, examining how sensitive data moves and what controls reduce that risk in transit and at rest. Mobile devices close the section as a deliberate final statement about the scope of modern defense-in-depth. BYOD and MDM are examined as the practical intersection of individual convenience and organizational risk.

Topics covered

  • Defense-in-Depth
  • IAM, Authentication and Password Security
  • Security Frameworks
  • Data Loss Prevention
  • Mobile Device Security

Labs

  • Password Auditing
  • Data Loss Prevention
  • Mobile Device Backup Recovery

Overview

Every compromise begins somewhere, and this section traces the full arc from vulnerability to response. It opens with vulnerability assessments and penetration testing, then examines modern attacks and malicious software with real-world examples of compromise. Web application security receives dedicated attention given the scale of risk web applications introduce. Security operations and log management address what happens after a foothold is gained: adversaries who gain access do not stop moving, and logging is the detection infrastructure that makes that movement visible. DNS threat hunting extends this detection focus directly into DNS traffic, where a meaningful share of command-and-control and exfiltration activity hides in plain sight. The section closes with digital forensics and incident response, the structured methodology for handling a compromise once it is found.

Topics covered

  • Vulnerability Assessments and Penetration Testing
  • Attacks and Malicious Software
  • Web Application Security
  • Security Operations and Log Management
  • Digital Forensics, Incident Response and DNS Threat Hunting

Labs

  • Network Discovery
  • Binary File Analysis and Characterization
  • Web App Exploitation
  • SIEM Log Analysis

Overview

There is no single technology that guarantees complete security, but cryptography addresses more security challenges than almost any other, when it is deployed correctly. This section opens with cryptographic concepts, algorithms, and deployment, then moves into applying cryptography to protect data in transit and at rest. The second half shifts to prevention and detection technologies at the network and endpoint level, including firewalls and intrusion prevention and detection systems. Network security monitoring tools such as Snort3 and Zeek are examined directly, including how they surface the presence of adversary emulation frameworks such as Cobalt Strike inside network traffic, a capability that sits at the center of the Network Analyst's detection role.

Topics covered

  • Cryptography
  • Cryptography Algorithms and Deployment
  • Applying Cryptography
  • Network Security Devices & Detecting Cobalt Strike
  • Endpoint Security

Labs

  • Hashing and Cryptographic Validation
  • Encryption and Decryption
  • Analyzing HTTPS
  • Intrusion Detection and Network Security Monitoring with Snort3 and Zeek

Overview

The Windows ecosystem has expanded well beyond simple desktop workgroups, now spanning on-premises Active Directory, Azure, PowerShell, Microsoft 365, Hyper-V, and more. This section builds a solid foundation in Windows security architecture, including Windows as a Service and the patch and update mechanisms that keep a modern Windows environment current. Access controls receive dedicated attention: NTFS and Active Directory permissions, privileges, and where implementation fails to match intent, along with BitLocker and hardware-based protections. Enforcing security configurations at scale follows, using Group Policy Objects and security templates to apply controls consistently across an environment. From there, the section shifts into Microsoft Azure, where many familiar on-premises concepts have direct cloud equivalents that behave, and fail, differently. Advanced authentication attacks are examined directly, connecting the access control discussion to the techniques adversaries use to defeat it. The section closes with scripting, automation, logging, and auditing, since manual administration does not scale to enterprise Windows environments, and PowerShell is the tool that closes that gap.

Topics covered

  • Windows Security Architecture
  • Windows as a Service
  • Windows Access Controls
  • Enforcing Security Configuration
  • Microsoft Cloud Computing
  • Advanced Authentication Attacks
  • Automation, Logging, and Auditing
  • Scripting and Automation

Labs

  • Windows Process Exploration
  • Windows Filesystem Permissions
  • Applying Windows System Security Policies
  • Using PowerShell for Speed and Scale

Overview

Linux systems are often fewer in number than Windows systems in a given environment, but they are frequently the most critical: database servers, web servers, and cloud infrastructure components disproportionately run on Linux. This section opens with Linux fundamentals and the command line, providing foundational grounding for those newer to the platform alongside practical guidance for administrators who manage it daily. Containers enter the discussion because Linux is where they were born. Built on the principle of minimization, containers offer deployment flexibility that has made them central to modern cloud computing, and this module examines what they represent for information security, what they do not, and how to manage them with appropriate security discipline. The section then extends into Linux security enhancements and infrastructure, including hardening, logging, and the utilities that extend what Linux provides by default. macOS closes the section with a review of its native security features and the genuine limitations that come with them, built on its UNIX foundation.

Topics covered

  • Linux Fundamentals
  • Linux Command Line
  • Containerized Security
  • Linux Security Enhancements and Infrastructure
  • macOS Security

Labs

  • Linux Permissions
  • Linux Containers
  • Linux Logging and Auditing

Virtual (OnDemand) | Self-Paced, 4 Months Access | $8,780 USD

Register

Things You Need To Know

Important! Bring your own system configured according to these instructions.

If you do not carefully read and follow these instructions, you will not be able to fully participate in the hands-on exercises. Please arrive with a system meeting all specified requirements.

Back up your system before class and ensure it contains no sensitive or critical data. SANS is not responsible for your system or data.

Mandatory System Hardware Requirements

  • CRITICAL: Apple Silicon devices (M-Series Chips) cannot perform the virtualization required for the labs and cannot be used for this course.
  • CPU: 64-bit Intel i5/i7 (8th generation or newer), or AMD equivalent. A 64-bit, 2.0+ GHz or newer processor is mandatory.
  • BIOS settings must enable virtualization technology, such as "Intel-VTx" or "AMD-V" extensions. Be absolutely certain you can access your BIOS/UEFI if it is password protected, in case changes are necessary.
  • 16GB of RAM or more is required.
  • 100GB of free internal storage space or more is required.
  • At least one available USB 3.0 Type-A port. A Type-C to Type-A adapter may be necessary for laptops with only USB-C ports. Some endpoint protection software prevents the use of USB devices, so test your system with a USB drive before class.
  • Wireless networking (802.11) is required. There is no wired Internet access in the classroom.

Mandatory Host Configuration and Software Requirements

  • Your host operating system must be the latest version of Windows 10, Windows 11, or macOS 10.15.x or newer (Intel-based Macs only).
  • Linux hosts are not supported in the classroom due to the variability of Linux configurations. If you choose to use Linux as your host, you are solely responsible for configuring it to work with the course materials and virtual machines.
  • Fully update your host operating system prior to class to ensure you have the correct drivers and patches installed.
  • Local Administrator access is required. If your organization will not permit this access for the duration of the course, arrange to bring a different laptop.
  • Ensure that antivirus or endpoint protection software can be disabled or fully removed, and that you have the administrative privileges to do so. These products can prevent successful lab completion.
  • Any filtering of egress traffic may prevent successful lab completion. Firewalls may need to be disabled — ensure you have the administrative privileges to do so.
  • Download and install VMware Workstation Pro 16.2.X+ (for Windows 10 hosts), VMware Workstation Pro 17.0.0+ (for Windows 11 hosts), or VMware Fusion Pro 12.2+ (for Intel-based macOS hosts) prior to class.
  • On Windows hosts, VMware products may not coexist with the Hyper-V hypervisor. For the best experience, ensure VMware can boot a virtual machine before class — this may require disabling Hyper-V. Instructions for disabling Hyper-V, Device Guard, and Credential Guard are included in the setup documentation accompanying your course materials.
  • Download and install 7-Zip (for Windows Hosts) or Keka (for macOS hosts – Intel-based ONLY). These tools are also included in your downloaded course materials.

Your course media is delivered via download. The media files for class can be large. Many are in the 30 GB range. You need to allow plenty of time for the download to complete. Internet connections and speed vary greatly and are dependent on many different factors. Therefore, it is not possible to give an estimate of the length of time it will take to download your materials. Please start your course media downloads as soon as you get the link. You will need your course media immediately on the first day of class. Do not wait until the night before class to start downloading these files.

Your course materials include a "Setup Instructions" document that details important steps you must take before you travel to a live class event or start an online class. It may take 30 minutes or more to complete these instructions.

Your class uses an electronic workbook for its lab instructions. In this new environment, a second monitor and/or a tablet device can be useful for keeping class materials visible while you are working on your course's labs.

If you have additional questions about the laptop specifications, please contact customer service.

MIL401N is designed for military, government, and defense personnel preparing to perform Network Analyst functions aligned to DCWF and DoD 8140 workforce requirements. The course is built for learners who need practical capability in traffic analysis, DNS and NDR/NSM threat hunting, and network-centric defensive cyber operations, not broad, general cybersecurity awareness.

You should attend if:

  • You are preparing for a Network Analyst, network security monitoring, or defensive cyber operations role
  • You are transitioning into cyber defense from another military, intelligence, IT, communications, or operational background
  • You support workforce development initiatives aligned to DCWF, DoD 8140, CFP, DCCF, or similar cyber workforce frameworks
  • You need hands-on training focused on packet analysis, DNS threat hunting, NDR/NSM, and network detection tooling
  • You are building or scaling network analyst capability across military, government, or defense cyber teams
  • You need a structured, role-aligned pathway into modern network defense operations using practical labs and operational scenarios

This training course aligns to NICE / DCWF workforce roles including:

  • Primary Alignment
    • Network Analyst (OPM 443)
    • Network Operations Specialist (OPM 441)
  • Supporting / Adjacent Roles
    • Cyber Defense Infrastructure Support Specialist (OPM 521)
    • Systems Security Analyst (OPM 461)

The GIAC Security Essentials (GSEC) certification validates a practitioner's knowledge of information security beyond simple terminology and concepts. GSEC certification holders are demonstrating that they are qualified for hands-on IT systems roles with respect to security tasks.

  • Defense in depth, access control and password management
  • Cryptography: basic concepts, algorithms and deployment, and application
  • Cloud: AWS and Azure operations
  • Defensible network architecture, networking and protocols, and network security
  • Incident handling and response, data loss prevention, mobile device security, vulnerability scanning and penetration testing
  • Linux: Fundamentals, hardening and securing
  • SIEM, critical controls, and exploit mitigation
  • Web communication security, virtualization and cloud security, and endpoint security
  • Windows: access controls, automation, auditing, forensics, security infrastructure, and services

More Certification Details

  • Coursebooks and lab workbook with over 500 pages of exercises
  • Virtual machines pre-installed with essential tools
  • TCP/IP reference guides
  • MP3 audio files of complete course lectures

The MIL401N course covers all the core areas of security and assumes a basic understanding of technology, networks, and security. For those who are new to the field and have no background knowledge, SEC275: Foundations - Computers, Technology and Security would be the recommended starting point. While this course is not a prerequisite for MIL401H, it does provide the introductory knowledge to help maximize the experience with MIL401H training.

MIL401N is part of a role-aligned Network Analyst workforce development pathway supporting network monitoring, DNS and NDR threat hunting, SOC operations, and defensive cyber operations aligned to DoD 8140 workforce requirements.

The course establishes the foundational operational capability required for Network Analyst roles and prepares learners for progression into more specialized network defense and monitoring training.

Depending on your operational role or workforce development pathway, recommended next steps include:

Networking Monitoring / SOC Progression

Incident Response / DFIR

Cloud and Defensive Infrastructure

Advanced Defensive Operations

Modern cyber defense operations depend on analysts who can monitor, detect, and hunt threats within network traffic across on-premises, cloud, and hybrid environments. Those capabilities are not built through isolated technical skills alone, they require a structured operational foundation aligned to how network defense is actually performed.

MIL401N establishes that foundation by developing the core technical and analytical capabilities required for Network Analyst roles aligned to DCWF and DoD 8140 workforce requirements. The course focuses on the operational disciplines that underpin effective network defense, including capturing and analyzing network traffic at the protocol and packet level, mapping DNS architecture and hunting for malicious DNS activity, working with NDR and NSM data sources to detect intrusions, recognizing adversary tooling including command-and-control frameworks such as Cobalt Strike, applying defensive controls across Windows, Linux, cloud, and wireless environments, and supporting network-centric defensive cyber operations through structured, workflow-driven analysis.

These are the capabilities that allow organizations to build scalable network analyst readiness across SOC and cyber defense teams. Without them, advanced tooling and specialized capabilities operate without the operational foundation required to use them effectively.

Cyber defense organizations increasingly need analysts who can contribute operationally from day one, not simply understand cybersecurity concepts in theory. MIL401H is designed to build the practical monitoring, detection, investigation, and response capabilities required for Host Analyst roles aligned to DCWF 463 / DoD 8140 workforce requirements.

Here is what that means in practice:
  • Build operational Cyber Defense Analyst capability: MIL401N is structured around how defensive cyber operations actually function: monitoring activity, analyzing events, investigating suspicious behavior, escalating incidents, and supporting response operations across network, endpoint, cloud, and hybrid environments.
  • Develop practical, hands-on analyst experience: The course uses realistic operational scenarios and hands-on labs to reinforce analyst workflows using SIEM processes, traffic analysis, logging, vulnerability investigation, defensive tooling, and incident response techniques. The emphasis is on operational readiness—not passive learning.
  • Prepare for modern SOC and cyber defense environments: Students develop practical familiarity with the technologies and workflows commonly used in modern cyber defense operations, including cloud infrastructure, defensive monitoring, AI-assisted analysis, and hybrid enterprise environments.
  • Establish a foundation for advanced defensive cyber operations training: MIL401N provides the operational and technical foundation required for progression into more advanced SOC, cyber defense, threat detection, DFIR, and cloud security training pathways.
  • Align to recognized workforce frameworks and career pathways: The course is aligned to Cyber Defense Analyst-style workforce requirements used across military, government, and defense organizations, helping students build capability directly relevant to operational cyber defense roles.
  • Learn skills that transfer immediately to operational environments: The labs, workflows, and scenarios in MIL401N are designed around realistic analyst activities and operational decision-making. Students return to work with practical capability they can apply immediately within SOC and cyber defense teams.

Benefits of Learning with SANS

Bryan Simon: Teacher Standing Next to Smartboard and Explaining Concept

Get feedback from the world’s best cybersecurity experts and instructors
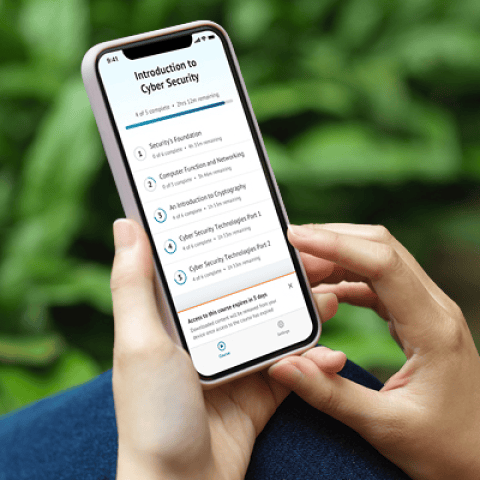
OnDemand Mobile App

Choose how you want to learn - online, on demand, or at our live in-person training events
Close Up of Woman Holding a Pen and Documents

Get access to our range of industry-leading courses and resources