SEC536: Adversarial AI - Penetration Testing AI Systems
SEC536Offensive Operations, Artificial Intelligence

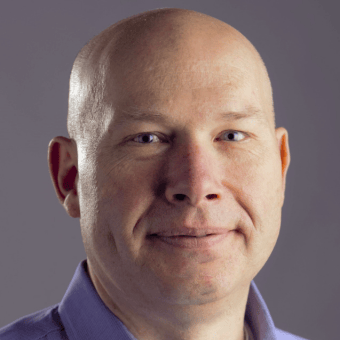
Chris Edmundson brings more than 25 years of IT, security operations, identity, architecture, and cloud security experience to SANS training, helping students connect tactical cloud defense to the operational decisions they face at work.
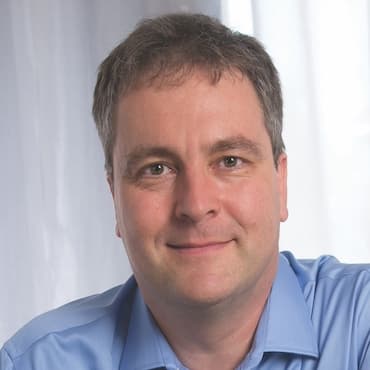
Dr. Johannes Ullrich is the Dean of Research for SANS Technology Institute, a SANS Faculty Fellow, and founder of the Internet Storm Center (DShield.org) which provides a free analysis and warning service to thousands of Internet users and organizations.
In-Person
In-Person
Leaders are entering an era where emerging technologies are reshaping not only cyber operations, but also decision-making, organizational trust, and resilience. Artificial intelligence is accelerating the speed and scale of cyber threats through automated reconnaissance, intelligent phishing, deepfake-enabled deception, and AI-assisted offensive operations. At the same time, the rapid adoption of AI systems is introducing new risks involving data integrity, model manipulation, autonomous agents, third-party dependencies, and the misuse of trusted digital platforms. Compounding these challenges is the rise of cognitive cyber operations, where adversaries use misinformation, synthetic media, and AI-generated content to influence personnel, disrupt public confidence, and manipulate strategic narratives. These threats increasingly target leadership decision cycles, employee behavior, and institutional credibility as much as traditional technical systems.
This session examines how AI-driven cyber capabilities, information manipulation, and digital trust risks are converging into a new generation of emerging threats relevant to leadership at every level. Attendees will gain insight into AI-enabled influence operations, synthetic identity and impersonation threats, the manipulation of trusted data, and the growing importance of resilience, governance, and cyber-informed leadership. The discussion focuses on practical leadership priorities for preparing organizations to operate securely and confidently in an increasingly contested digital environment.
Learning Objectives:
In-Person
In 2026, the question of whether adversaries can reach Canadian operational technology has been answered. CSE has confirmed that a Russian-aligned group accessed a Quebec water treatment facility and reached the controls for pumps and chlorine dosing. The same pattern is playing out across the energy, water, and manufacturing systems Canadians rely on every day.
This session gives government attendees a current picture of the OT threat environment: the groups active against North American critical infrastructure, how they get into industrial control systems and stay there, and what a year of frontline incident response and threat intelligence from Dragos says about where defences fail.
Canada's response is taking legal shape. With Bill C-8 now law and the Critical Cyber Systems Protection Act obligations approaching for designated operators in pipelines, power, nuclear, transport, and beyond, Peter examines what the legislation demands of OT environments and where the gaps between compliance and defence will appear.
Then, what works. Using the SANS Five ICS Cybersecurity Critical Controls as the frame, Peter walks through the defensive priorities that matter most, where AI is changing the equation for attackers and defenders alike, and the concrete steps government stakeholders can take now.
In-Person
In-Person
Everything is a web application; you may not realize it, but attackers do. Your enterprise security appliance, your AI tools, and your ERP are all susceptible to the same types of attacks, and AI is accelerating exploit development. For example, WordPress vulnerabilities that used to cost $500,000 to develop can now be had for a mere $25 in AI tokens. In this talk, we will walk through the development of an exploit for a recent vulnerability, show how attackers exploited it, and explain how defenders must proactively deploy security controls to defend against this new breed of attacks. The talk will switch between the attackers' and defenders' points of view to illustrate how defenses work and how attackers may attempt to bypass them. You will learn how to better defend against the “unknowns” presented by this new breed of attacks and how to detect these attacks early. The talk will include live demonstrations of how these attacks and defenses work.
In-Person
In-Person