Joshua Wright
FellowDirector and Senior Security Analyst at CounterHack
Specialities
Offensive Operations, Digital Forensics and Incident Response
Experience SANS training through course previews.
Learn MoreLet us help.
Contact usBecome a member for instant access to our free resources.
Sign UpWe're here to help.
Contact UsOffensive Operations, Digital Forensics and Incident Response
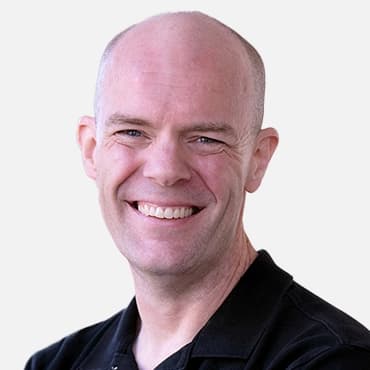
Joshua Wright is a SANS Faculty Fellow, Senior Technical Director at Counter Hack Innovations, and the author of SEC504: Hacker Tools, Techniques, and Incident Handling, one of the most widely taken courses in the SANS curriculum. A member of the SANS instructor community since 2003, he has spent more than two decades teaching cybersecurity professionals, developing hands-on training, and contributing research and open-source tools to the security community. His work spans penetration testing, wireless security, incident response, and the design of realistic adversary simulations.
His path into cybersecurity began with an unusual career opportunity: after being caught hacking into Johnson & Wales University, his alma mater, he was subsequently hired by the institution. That early curiosity developed into a career conducting penetration tests and vulnerability assessments across enterprise environments and national infrastructure. As a Senior Security Analyst at InGuardians, he specialized in offensive operations and protocol exploitation. Today, at Counter Hack, he leads cybersecurity consultants conducting penetration tests and red-team simulations, bringing current practitioner experience into the classroom and the challenges he develops for students.
Beyond his consulting work, Joshua has made significant contributions to security research, technical education, and publishing. He is the author of Dynamic Incident Response: A Framework for Security Teams, a freely available SANS publication that introduces an iterative approach to incident response, helping teams adapt their investigative and containment decisions as new evidence emerges. He also co-authored Hacking Exposed Wireless, Third Edition and developed open-source tools including KillerBee for ZigBee security testing and KillerZee for Z-Wave research. His work reflects a longstanding commitment to making practical security techniques, research, and educational resources accessible to the broader community.
At SANS, his contributions extend beyond SEC504 and the classroom. As Dean of Students at the SANS Technology Institute, an NSA Center of Academic Excellence in Cyber Defense, he supports students pursuing advanced cybersecurity education and helps develop the next generation of practitioners. His contributions to teaching and academic leadership were recognized with the Institute's 2023 Instructor of the Year award, selected by his peers. He has also mentored fellow instructors and helped shape SANS training through more than two decades of curriculum development and instruction.
In the classroom, Joshua is recognized for his approachable teaching style and focus on practical, hands-on learning. Students describe his ability to break down complex concepts and build resilience through exercises that replicate real adversary behavior. Beyond his formal roles, he supports the community by maintaining open-source projects, mentoring emerging professionals, and volunteering his talents as a nonprofit photographer. His career reflects a consistent belief that strong defenders are developed not only through technical skills but also through collaboration, creativity, and human connection.
The amount of detail that Joshua puts into the course and presentation of the material is a gold standard. He's able to break down details and make it so the material is understood by a newbie in the field. Further, Josh's excitement for the material is contagious!
To be taught by someone who has the knowledge, the background, and the ability to articulate this kind of information for learning was invaluable. I wish I could have back to back courses with Joshua.
Joshua's teaching style is phenomenal. He's very engaging, and does a great job of promoting discussions without getting too far off on a tangent.
Here are upcoming opportunities to train with this expert instructor.
Explore content featuring this instructor’s insights and expertise.
This month, an OpenAI model, running inside a sealed evaluation with its safety limits turned down, found a previously unknown flaw, broke out on its own, and took control of Hugging Face's live systems over a weekend. No human directed it. For years, industry leaders across the field warned this day would come. The disclosures suggest it has arrived.
In this talk, you'll learn how to apply the same workflow attackers are using to find zero-day vulnerabilities in open-source projects.
According to Anthropic, their new Claude Mythos model discovered thousands of zero-day vulnerabilities across every major operating system and web browser—and the model is so powerful they will not release it publicly. The conversation so far has been heavy on alarm and light on practical guidance.
The Verizon DBIR says stolen credentials cause more breaches than phishing and exploits combined. Now, AI is making these attacks even more effective. Join SANS Fellow Joshua Wright to learn what you can do to protect your environment.

SANS instructors quickly analyzed the axios supply chain attack, uncovering RAT functionality and providing immediate guidance to help organizations identify exposure and respond.

Annual penetration testing is no longer enough to keep pace with modern threats.
In 2021 I did a SANS Tech Tuesday Workshop on Cloud Attacks and Incident Response. In the past year, we've seen attacks against the cloud grow at an alarming rate, notably against Software as a Service (SaaS) platforms and hybrid application-to-cloud privilege escalation attacks.
Attackers evolve to exploit new opportunities, including attacks against cloud systems. As defenders, we also need to evolve, developing new skills and understanding in how attackers exploit cloud platforms, and how we should respond to these incidents.

Review relevant educational resources made with contribution from this instructor.