Group Purchasing
Group Purchasing

SEC555 Live Online February

  • Mon, Feb 8 - Fri, Feb 12, 2027
  • 1 Course
  • English
Virtual (ET)
SEC555: SIEM with Tactical Analytics
  • 5-Day Course: February 8 – 12, 2027

    Earn 30 CPEs.

  • GIAC Certified Detection Analyst
  • Intermediate Skill Level

    Course material is geared for cybersecurity professionals with hands-on experience.

  • 18 Hands-On Labs

    Apply what you learn with hands-on exercises and labs.

SEC555: Detection Engineering and SIEM Analytics - Live Online with Course Author Nick Mitropoulos

Security operations does not have a data problem. It has an analysis problem. The logs are already flowing; the question is whether anything in them would tell you an attack was underway.

SEC555 is five days of live, virtual instruction on building detections that answer that question. You construct your own detection lab, learn to read logs for what they actually contain, write rules that fire on the behavior you meant to catch, and build a pipeline that gets new content into production without a six-week wait. Cloud and on-premises sources are treated as one problem, because that is how they arrive.

During the week, you'll work through:

  • 18 hands-on labs
  • A team-based Defend the Flag capstone
  • DeTTECT data source gap analysis and honeypot deployment
  • DNS, HTTP, Windows, and auditd log investigation exercises
  • Cobalt Strike beaconing detection and malicious PowerShell identification
  • Microsoft Sentinel, KQL, CloudTrail, and CloudWatch configuration and testing

AI-Assisted Detection Engineering

The final section covers automated detection engineering pipelines, CI/CD workflows for detection content, and using large language models to assist rule authoring without handing over the judgment. 30 CPE credits, aligned to the GIAC Certified Detection Analyst (GCDA) certification.

Who Should Take This Course?

Detection engineers and detection analysts, SOC and security analysts, security engineers, threat hunters, incident responders, and security architects who own monitoring coverage. A working understanding of TCP/IP, logging methods, and operating system fundamentals is the baseline.

Download the Course Syllabus or Letter to Justify this Training to Your Manager

To learn more about SEC555, business takeaways, laptop requirements and more, please visit the course page.

Early Bird Offer

Save $750 USD using the code "EarlyBirdNA" and pay for any 4-6 day course (excluding Beta Courses and 300 Level Courses) by October 20, 2026.

Courses

Looking for Group Purchasing? Contact Sales

Featured Speaker

Nick Mitropoulos
Nick Mitropoulos

Nick Mitropoulos

CEO at Scarlet Dragonfly

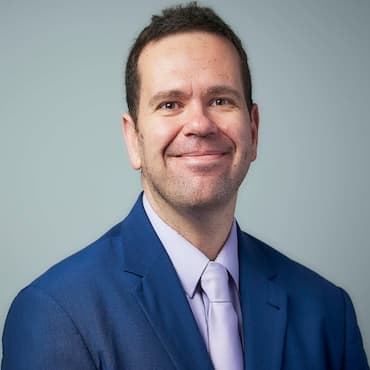
Nick Mitropoulos is a SANS Certified Instructor and author of SEC555: Detection Engineering and SIEM Analytics. As CEO of Scarlet Dragonfly and a veteran of SOC and incident response leadership, he equips students with real-world skills in detection engineering. Nick also serves on the GIAC Advisory Board, SANS CISO Network, and faculty of the SANS Technology Institute.

Read more about Nick Mitropoulos

Three Reasons to Train Virtually

  • Ultimate Convenience

    Eliminate the hassle of daily commutes and wasted travel time. You’ll have everything you need right from your home.

  • Personalization

    Hands-on learning with the opportunity to ask questions and receive instant feedback from world-renowned experts. Afterward, reinforce your skills with 4-months of access to daily course lecture archives.

  • Hands-On Labs

    Learn cutting-edge cybersecurity knowledge with hands-on labs that provide you with techniques you can immediately use in your organization.

Woman at Laptop