Group Purchasing
Group Purchasing

Welcome to ICS612: ICS Cybersecurity In-Depth

Monday, January 12 - Friday, January 16, 2026 Ottawa Conference and Event Centre 200 Coventry Road. Ottawa, ON K1K 4S3 Canada

In Person | Instructor: Jason Dely | 25 Hand-On Labs | 30 CPEs

Develop comprehensive defenses in industrial control systems, and master methodologies through hands-on exercises in a simulated operational technology environment with real-world components.

Course Overview

Securing Operational Technology (OT) vs. IT environments requires a different perspective and approach. Each OT system is uniquely engineered to an organization's operational needs, so how should we go about securing these systems?

Through our immersive operations environment, ICS612 will take you from theory to practice over this five-day ICS security training course. You will learn to identify operational vulnerabilities and build defenses in the roles of engineering, operations, and red and blue teams. You will navigate from PLC and HMI operations to the complexities of advanced IT and OT security architecture and monitoring, understanding how threat actors attack operations through ICS systems and personnel. You will reinforce these skills in hands-on lab exercises and conclude with an incident response scenario investigating and recovering classroom operations.

Emerge with a thorough understanding of how to analyze an unknown system to secure and maintain operational resilience.

A Comprehensive Deep Dive into Securing Industrial Environments

Hands-on labs drive this course’s key concepts and learning objectives. The in-classroom lab setup was developed to simulate a real-world environment where a controller is monitoring/controlling devices deployed in the field along with a field-mounted touchscreen Human Machine Interface (HMI) available for local personnel to make needed process changes. Utilizing operator workstations in a remotely located control center, system operators use a Supervisory Control and Data Acquisition (SCADA) system to monitor and control the field equipment. Representative of a real ICS environment, the classroom setup includes a connection to the enterprise, allowing for data transfer (i.e., Historian), remote access, and other typical corporate functions.

This advanced ICS security training course moves students through a variety of exercises that demonstrate how an attacker can exploit the unfortunately common vulnerability of a poorly architected ICS, and how defenders can secure and manage the environment effectively.

What You'll Learn

  • Learn active and passive methods to safely gather information about an ICS environment
  • Identify vulnerabilities in ICS environments
  • Determine how attackers can maliciously interrupt and control processes and how to build defenses
  • Implement proactive measures to prevent, detect, slow down, or stop attacks
  • Understand ICS operations and what "normal" looks like
  • Build choke points into an architecture and determine how they can be used to detect and respond to security incidents
  • Manage complex ICS environments and develop the capability to detect and respond to ICS security events

Business Takeaways

  • Enhance operational resilience in critical infrastructure
  • Reduce risk of costly production outages
  • Protect intellectual property and operational data
  • Meet regulatory compliance requirements
  • Improve threat detection capabilities
  • Build security into system architecture
  • Develop incident response capabilities for OT incidents

Meet Your Instructor

Jason Dely
Jason Dely

Jason Dely

Director at ICS Solutions

Jason Dely brings over 20 years of experience and a diverse industrial control system background to SANS and the industrial control system (ICS) community.

Read more about Jason Dely

Course Syllabus

This section aligns students to the baseline fundamentals of industrial control systems, focusing on local process control components, such as Programmable Logic Controllers (PLCs) and Human Machine Interfaces (HMIs).

Topics covered

  • Purdue model and ICS architecture
  • Communication flow mapping
  • Level 0-2 components
  • Protocol analysis of operations data
  • Embedded device security essentials

Labs

  • PLC and HMI platform setup
  • PLC programming and troubleshooting
  • Service discovery on controllers
  • OT protocol analysis with Wireshark
  • PLC/HMI communication analysis

Overview

Learning Objective - Review of Lab Setup

  • Students will become familiar with the Programmable Logic Controller (PLC), I/O, and software used in the lab.
  • Goal: Students will learn and review ICS nomenclature and terminology and set up their lab station.

Learning Objective - Introduction to the PLC Platform Application Tools

  • Use ICS software to download and operate an existing PLC project.
  • Walk through the basic PLC programming terminology.
  • Download a new firmware file and download and run an existing project file.
  • Interact with the PLC and demonstrate an error in the program.
  • Goal: Students will understand the tools required to have a functional PLC. They will begin to understand the operational relationships between ICS hardware and software.

Learning Objective - Introduction to Programming a PLC

  • Carried over from the previous lab, troubleshoot and fix the programming error.
  • Apply the fix and verify correctness.
  • Observe lack of required authentication, or use of weak credentials in ICS.
  • Goal: Students will understand what is required to modify the logic in a PLC. They will begin to learn some of the attack surface of the PLC.

Learning Objective - Service Discovery on PLC

  • Using NMAP, discover the services available on the PLC.
  • Where possible, interact with those identified services.
  • Determine the purpose and use of each available service.
  • Goal: Students will understand what services are available, the purposes they serve, and their criticality. They will expand their knowledge of the attack surface of the PLC.

Learning Objective - Introduction to the HMI Platform Application Tools

  • Use the ICS software to download and operate an existing HMI project.
  • Walk through the basic HMI programming terminology through an existing project.
  • Interact with the HMI and correlate the HMI configuration (objects/tags) with the PLC program.
  • Goal: Students will understand how a basic HMI operates. They will also learn the data relationships between PLC and HMI used in later labs.

Learning Objective - Understand HMI to PLC Communication

  • Using Wireshark, capture and dissect the ICS communication between the HMI and PLC.
  • Correlate the traffic with how the configuration of these devices transfer data over Ethernet.
  • Build foundational knowledge needed to build a network-level attack against the system.
  • Goal: Students will learn how data flows between PLC and HMI on the network. They will also begin to understand the weakness within ICS protocols.

Full Topic Details

  • Process familiarization using the Purdue model
  • Communication flow mapping referencing the Zones and conduit approach
  • Components of Level 0-2
  • Local I/O and local HMI communications
  • Understand operational functions
  • Understand inherent process weaknesses
  • Protocol dissection of operational data
  • Embedded device essentials
  • Operator Interface (I/O) subsystems and communications
  • Safety systems
  • Process time

This section explores how multiple control systems interact in a larger industrial environment and the security implications. Students will understand peer-to-peer communications in ICS, Supervisory Control and Data Acquisition (SCADA) systems, and Open Platform Communications (OPC).

Topics covered

  • Level 3 system components
  • PLC peer-to-peer communications
  • SCADA/OPC communications
  • IT service dependencies in OT
  • Defense techniques for Level 3

Labs

  • Zone/Cell/Area network connections
  • SCADA system configuration
  • OPC security configuration
  • Securing traditional IT services
  • Defending against Level 3 attacks

Overview

Learning Objective - Introduction to Peer-to-Peer Communications

  • Set up a Zone/Cell/Area to the larger Level 3 classroom "Production System" ICS network
  • Connect to a central L3 router, monitor its system, and establish peer-to-peer system communications.
  • Detect additional PLC attacks from the Level 3 system and configure defenses to thwart the attack.
  • Goal: This lab will help students recognize the relationships between Zones/Cells/Areas. Just like in the real world, students will communicate with owners of adjacent systems to map out baseline communications within an ICS.

Learning Objective - Introduction to SCADA Systems

  • Identify components of a SCADA system and the components of the classroom "Production System" setup.
  • Walk through the common use cases and weaknesses and defenses of traditional IT network services, including Active Directory, DNS, DHCP, NTP, SMB, etc.
  • Goal: Students will learn the components and communications of a SCADA system. They will also learn the overlap and use of traditional IT technologies within ICS.

Learning Objective - OPC Communications

  • Configure, or validate, the connectivity between the OPC server and their local PLC.
  • Create an OPC client connection from its local station to the OPC server at the front of the room.
  • Observe an OPC exploit against the system and navigate and configure the local Operating System security configurations to mitigate exploit.
  • Goal: Students will learn the common OS components, weaknesses of OPC communications, and possible defenses.

Full Topic Details

  • Learn components of Level 3
  • Learn peer-to-peer communications between PLCs
  • Learn SCADA/OPC communications
  • Learn the use and dependencies of traditional IT services (DNS, AD, DHCP, NTP, etc.)
  • Vendor security models and industrial DMZs
  • Learn attack vectors and defense techniques from Level 3

This section focuses on designing and implementing secure network architecture for industrial control systems. Students will understand and practice the deployment of common IT network technology in ICS.

Topics covered

  • Connected process security
  • Secure plant design principles
  • Industrial network segmentation
  • Trusted communications flows
  • Remote access and historian security

Labs

  • Network segmentation implementation
  • Firewall configuration for ICS
  • Data diode implementation
  • Historian system hardening
  • Jump host and 2FA implementation

Overview

Learning Objective - Network Architecture and Technology in ICS

  • Learn the weaknesses and defense options (i.e., segmentation) for a flat ICS network.
  • Identify service and communication requirements between Level 2 and 3 and build appropriate segmentation/defenses.
  • Invoke an attack on the system and configure and compare the differences between stateful and stateless ACLs.
  • Goal: Students will learn how common IT network technology is deployed in the environment, its common weaknesses, and defense strategies. Student will learn some basic (yet highly overlooked) firewall settings to build a defensive perimeter.

Learning Objective - ICS Firewalls

  • Implement in-line firewall.
  • Implement data diode.
  • Management network (iLo, Remote Management, Lantronix).

Learning Objective - ICS Perimeter

  • Learn methods to map ICS data flows and communication paths.
  • Identify and architect networks that support ICS business requirements.
  • Learn methods to restrict/reduce ICS network access to support minimal operations.
  • Learn common use cases; Historian, Remote Access, and Telemetry.

Learning Objective - Historians

  • Identify the business requirements for Historian systems.
  • Observe Historian system compromise and modify the architecture and configuration to defend.
  • Goal: Students will learn the components of a Historian system. They will learn how to securely architect, configure, and operate a Historian system into an ICS environment.

Learning Objective - Remote Access and Jump Host/2FA

  • Identify the business requirements for remote access.
  • Observe remote access compromise and modify system architecture, configure a jump host sever, and implement 2FA access to mitigate.
  • Goal: Students will learn how to securely architect, configure, and operate a jump host providing access into an ICS environment.

Full Topic Details

  • Understand connected process
  • Analyze case studies in ICS environments and secure plant design
  • Identify typical trusted communications flows (Time, File sharing, Remote Access, Historians, AD replication, Reverse Web Proxies, Patch servers)

This section addresses the ongoing management and monitoring of industrial control systems to maintain security. Students will understand and practice ICS system monitoring and logging, asset management, and asset validation.

Topics covered

  • ICS environment logging strategies
  • Monitoring and alerting best practices
  • Serial network security monitoring
  • System integrity verification
  • Asset management for OT systems

Labs

  • Log aggregation configuration
  • Event monitoring tuning
  • Asset management implementation
  • System integrity verification
  • Change management procedures

Overview

Learning Objective - ICS System Monitoring and Logging

  • Establish logging and alerting of local process assets into the environment log aggregator.
  • Goal: Students will ensure logged events are tuned for "events of interest" and implement industry-leading tools to view and detect abnormal behavior.

Learning Objective - ICS Asset Management

  • Evaluate patching and change management strategies and solutions to ensure asset management and system integrity visibility.
  • Goal: Students will learn how to manage a complex set of ICS assets and develop the capability to detect and respond to security events occurring at the control system level.

Learning Objective - ICS Asset Validation

  • Evaluate approaches to ensure or restore the integrity of a system to a known good state.
  • Goal: Students will evaluate the pre-work necessary for an organization to have the ability to return a compromised system to a reliable operating state.

Full Topic Details

  • Logging and traffic collection in an ICS environment
  • Monitoring and alerting in ICS networks
  • Monitoring and alerting in a serial network
  • System integrity verification

This final section tests students' skills through a NetWars-style comprehensive incident response scenario in the classroom ICS environment.

Topics covered

  • OT environment attack patterns
  • Protocol-level manipulation techniques
  • Firmware security considerations
  • Industrial wireless security
  • Time synchronization security

Labs

  • ICS NetWars-style challenge
  • Four levels of questions
  • Local process and share process
  • Head end process environment
  • Environment manipulation

Overview

Learning Objective - Hands on environment troubleshooting

Attack/Defend - ICS NetWars Style Challenge

  • Level 1: questions on local process
  • Level 2: questions on shared process
  • Level 3: questions on the head end process environment
  • Level 4: questions on environment manipulation

Full Topic Details

  • Pivoting and positioning in an ICS target environment
  • Operational traffic reverse engineering
  • Protocol-level manipulation
  • Firmware manipulation
  • Industrial wireless discovery and attack
  • Time synchronization manipulation
  • Data table and scaling modifications

The capstone is a full day of challenging hands-on work applying the principles taught throughout the course. Your team will progress through multiple levels and missions designed to ensure the presence of detection and defensive capabilities.

Full Topic Details

  • Applying Previously Covered Security Controls In-depth
  • Applying and fine-tuning detection capabilities and using automation to reduce false/positive ratio
  • Configuration management tools
  • Infrastructure as code templates
  • Tines playbook development
  • AWS Configuration rules & ARM templates

Things You Need To Know

Important! Bring your own system configured according to these instructions.

A properly configured system is required to fully participate in this course. If you do not carefully read and follow these instructions, you will not be able to fully participate in hands-on exercises in your course. Therefore, please arrive with a system meeting all of the specified requirements.

Back up your system before class. Better yet, use a system without any sensitive/critical data. SANS is not responsible for your system or data.

Mandatory System Hardware Requirements

  • CPU: 64-bit Intel i5/i7 (8th generation or newer), or AMD equivalent. A x64 bit, 2.0+ GHz or newer processor is mandatory for this class.
  • CRITICAL: Apple Silicon devices cannot perform the necessary virtualization and therefore cannot in any way be used for this course.
  • BIOS settings must be set to enable virtualization technology, such as "Intel-VTx" or "AMD-V" extensions. Be absolutely certain you can access your BIOS if it is password protected, in case changes are necessary.
  • 16GB of RAM or more is required.
  • 150GB of free storage space or more is required.
  • At least one available USB 3.0 Type-A port. A Type-C to Type-A adapter may be necessary for newer laptops. Some endpoint protection software prevents the use of USB devices, so test your system with a USB drive before class.
  • Wireless networking (802.11 standard) is required. There is no wired Internet access in the classroom.
  • A wired Ethernet network adapter is required for this course. This can be either an internal or an external USB-based network adapter but you cannot use wireless networking alone.

Mandatory Host Configuration And Software Requirements

  • Your host operating system must be the latest version of Windows 10, Windows 11, or macOS 10.15.x or newer.
  • Fully update your host operating system prior to the class to ensure you have the right drivers and patches installed.
  • Linux hosts are not supported in the classroom due to their numerous variations. If you choose to use Linux as your host, you are solely responsible for configuring it to work with the course materials and/or VMs.
  • Local Administrator Access is required. (Yes, this is absolutely required. Don't let your IT team tell you otherwise.) If your company will not permit this access for the duration of the course, then you should make arrangements to bring a different laptop.
  • You should ensure that antivirus or endpoint protection software is disabled, fully removed, or that you have the administrative privileges to do so. Many of our courses require full administrative access to the operating system and these products can prevent you from accomplishing the labs.
  • Any filtering of egress traffic may prevent accomplishing the labs in your course. Firewalls should be disabled or you must have the administrative privileges to disable it.
  • Microsoft Office (any version) or OpenOffice installed on your host. Note that you can download Office Trial Software online (free for 30 days).
  • Download and install VMware Workstation Pro 16.2.X+ or VMware Player 16.2.X+ (for Windows 10 hosts), VMware Workstation Pro 17.0.0+ or VMware Player 17.0.0+ (for Windows 11 hosts), or VMWare Fusion Pro 12.2+ or VMware Fusion Player 11.5+ (for macOS hosts) prior to class beginning. If you do not own a licensed copy of VMware Workstation Pro or VMware Fusion Pro, you can download a free 30-day trial copy from VMware. VMware will send you a time-limited serial number if you register for the trial at their website. Also note that VMware Workstation Player offers fewer features than VMware Workstation Pro. For those with Windows host systems, Workstation Pro is recommended for a more seamless student experience.
  • On Windows hosts, VMware products might not coexist with the Hyper-V hypervisor. For the best experience, ensure VMware can boot a virtual machine. This may require disabling Hyper-V. Instructions for disabling Hyper-V, Device Guard, and Credential Guard are contained in the setup documentation that accompanies your course materials.
  • Download and install 7-Zip (for Windows Hosts) or Keka (for macOS hosts). These tools are also included in your downloaded course materials.

Your course media is delivered via download. The media files for class can be large. Many are in the 40-50GB range, with some over 100GB. You need to allow plenty of time for the download to complete. Internet connections and speed vary greatly and are dependent on many different factors. Therefore, it is not possible to give an estimate of the length of time it will take to download your materials. Please start your course media downloads as soon as you get the link. You will need your course media immediately on the first day of class. Do not wait until the night before class to start downloading these files.

Your course materials include a "Setup Instructions" document that details important steps you must take before you travel to a live class event or start an online class. It may take 30 minutes or more to complete these instructions.

If you have additional questions about the laptop specifications, please contact customer service.

ICS612 training is recommended for a diverse range of individuals, including:

  • ICS410 Course Alumni - Students who have successfully completed ICS410: ICS/SCADA Security Essentials will have the base knowledge considered as a prerequisite for this course.
  • Process Control Engineers
  • Systems or Safety System Engineers
  • Active Defenders in ICS
  • Anyone with significant control system experience interested in understanding processes and methods to secure the ICS environment

A fully functional SANS ICS612 Student Kit that students will keep after class:

    • A CLICK PLC Plus Controller including an additional temperature input module and thermocouple
    • Commercial Click PLC Programming software from KOYO Electronics.
    • A C-More HMI Operator Interface with HMI development software
    • Physical components and attachments for I/O connections to the SANS student kit.
    • A highly modified Useless box used as a input device to the Click Plus PLC controller. Useless box can be used in standalone mode as well.
  • International power connector kit
  • A SANS ICS612 Windows Virtual Machine.
  • A SANS ICS612 Kali Virtual Machine.
  • A SANS ICS612 Relics Virtual Machine
  • Access to the in-class physical ICS range running automation support software such as distributed HMIs, OPC Servers, operational trending software and network monitoring solutions.

ICS612 is an advanced course that focuses on the engineering, implementation, and support of secure control system environments. Students taking ICS612 should have completed ICS410: ICS/SCADA Security Essentials or should have a strong understanding of the objectives taught in that course. The course also builds upon the skills learned in ICS515: ICS Visibility, Detection, and Response, and ICS612 students should have working knowledge of network security monitoring and data collection techniques.

With your purchase of this ICS Security course, you will receive complimentary OnDemand access to ICS310: ICS Cybersecurity Foundations — an added benefit, not a prerequisite or requirement. This course is a great way to reinforce key concepts or fill gaps in your ICS/OT security knowledge, whether you complete it in full or focus on what’s most relevant to you. Within 14 business days, you will receive a non-transferable access code via your SANS account email.

The recommended learning path begins with ICS410: ICS/SCADA Security Essentials to build foundational knowledge. ICS612 builds on this foundation with advanced hands-on skills. For optimal career development, continue on to ICS515 for incident response capabilities or ICS456 for regulatory compliance expertise in critical infrastructure protection.

Industrial Control System Security is the practice of protecting operational technology environments that manage critical infrastructure and industrial processes. It requires specialized knowledge of both cybersecurity and industrial operations, focusing on maintaining system availability, integrity, and confidentiality while ensuring safety and reliability of physical processes that impact the real world.

This ICS security training course will elevate students’ careers by providing hands-on experience with actual industrial components and security techniques specific to OT environments. Participants develop specialized skills highly sought after by critical infrastructure sectors, manufacturing, and energy companies. The practical knowledge gained enables attendees to bridge the IT/OT gap and implement effective security controls in environments where downtime can have severe consequences.

Pricing & Registration

This class is In Person only, please click the "Register Now" button below.

Please note that these links will take you to the login page for a SANS account. If you have a SANS account, please enter your Username and Password to register for the class. If you do not have a SANS account, you will need to create one before registering.

Man Working on Laptop

Benefits of Learning with SANS

Bryan Simon: Teacher Standing Next to Smartboard and Explaining Concept

Get feedback from the world’s best cybersecurity experts and instructors
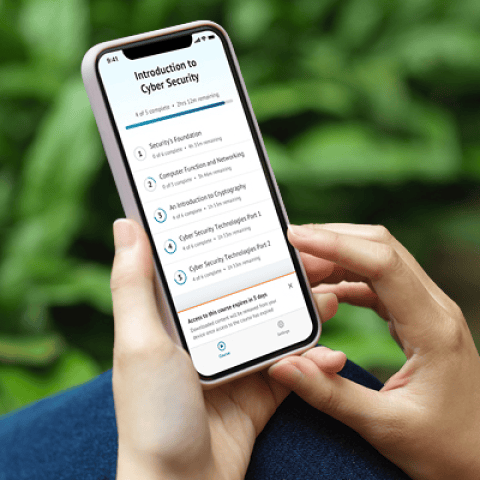
OnDemand Mobile App

Choose how you want to learn - online, on demand, or at our live in-person training events
Close Up of Woman Holding a Pen and Documents

Get access to our range of industry-leading courses and resources
Ottawa ICS612 | January 2026 | SANS Institute
